




Shadow IT is any hardware, software or IT resource running inside your organization that the IT department never approved, never configured and, in most cases, does not know exists. It covers the file sharing account someone opened with a departmental card, the personal laptop plugged into the office network, and the AI assistant installed on a work machine last Tuesday. None of it is necessarily malicious, and all of it sits outside every control you have.
If you cannot name what is running, you cannot patch it, license it, budget for it or answer for it in an audit. This guide covers how to manage shadow IT in practice: detecting it from the IT Asset Management (ITAM) inventory you already run, writing a policy people follow, and deciding what to do with each unapproved tool once it surfaces.
Gartner reported in 2023 that 41% of employees had acquired, modified or created technology outside IT’s visibility during 2022, and predicted that share would reach 75% by 2027. With 2027 close, that prediction is about to be tested. The two sections below cover what shadow IT looks like in practice and why the unknown itself is the problem.
Shadow IT rarely arrives as a deliberate breach of policy. It usually starts with someone solving a real problem faster than the official route would allow. The categories that recur across most organizations are:
Each of these leaves a different trace, which is why no single detection method finds all of them. Installed software shows up on the endpoint, while a browser-only service may never appear anywhere except an expense report.
The UK National Cyber Security Centre frames the risk more precisely than most definitions do: "There might not be a risk, there might be a critical risk. The organisation simply doesn’t know. Shadow IT is therefore an unmanaged risk." A sanctioned tool with a known flaw can be sized and scheduled, while an unsanctioned one is a blank space on the map. The practical consequences are data leaving through services with no contract, licenses paid for twice, endpoints missing from patch cycles, and audit questions nobody can answer.
There is an argument on the other side, and the same guidance makes it: employees resorting to insecure workarounds to get the job done suggests existing policies need refining. Read that way, each unapproved tool is also feedback about a gap in what IT offers. It is worth separating this from Bring Your Own Device (BYOD) programs, which involve the same devices under a very different regime of enrollment, acceptable use agreements and some control over corporate data, none of which exists when nobody knows the asset is there.
Shadow IT detection works best as a set of overlapping passes rather than one scan. Each pass covers a different class of asset, and the value of running them together is that anything appearing in one source and missing from another becomes a candidate for review. The passes below move from the network outward to the accounts and the spending.
The first pass answers a narrow question: what is connected that the inventory does not hold? A network scan walks the address ranges you define and reports everything that answers. Because it works over protocols such as DNS, ICMP, SNMP, TCP and UPnP, it also reaches hardware that cannot run software of its own.
This is how unregistered laptops, consumer routers, printers and IP phones surface. Anything the scan finds and the inventory does not list goes into a review queue, which is the same workflow that rogue device detection follows more broadly.
A network scan tells you a machine exists. An agent installed on that machine tells you what is running on it, reporting every installed application rather than only the ones IT provisioned.
This is the pass that finds unapproved software on managed hardware, and it usually produces the longest list. Running it on a schedule turns automated software discovery into a standing control instead of an annual exercise.
A list of installed software is raw data until it is measured against something. It becomes a finding when you compare it to a classification of what is allowed, what is under review and what is prohibited.
Two comparisons matter. Installed against authorized surfaces policy violations, and installed against licensed surfaces compliance exposure along with software nobody paid for. That overlap is why a software audit and a shadow IT sweep usually turn up the same names.
Software that never touches an endpoint leaves its trace somewhere else. Subscription records, expense claims and identity provider logs reveal tools a device scan will never see, which is where most unsanctioned SaaS lives.
Three sources are worth pulling on a schedule:
Read together, these answer who is using what and whether the organization is paying twice for the same capability. That is the ground SaaS governance covers once the discovery work is done.
Being clear about the limits keeps the exercise honest. An asset inventory sees installed software and connected devices, and it does not see a browser tab.
Three blind spots are worth tracking separately:
Identity provider logs and outbound traffic monitoring cover most of that ground, and both sit outside the asset inventory. Naming the boundary up front is what keeps the inventory-based passes credible for everything they do cover.
Unsanctioned AI tools are shadow IT with a shorter adoption cycle and a larger data surface. Gartner reported in November 2025 that 69% of organizations suspect or have evidence that employees are using prohibited public generative AI. The National Cyber Security Centre now names it directly in its shadow IT guidance, describing unmanaged AI services such as chatbots being used with corporate data.
For detection purposes the distinction that matters is where the tool runs. An AI application installed on a managed machine reports like any other executable and appears in the same pass that finds unapproved software, while an assistant used in a browser tab under a personal account produces no inventory record at all. The second case belongs to the identity and traffic signals above, which is why an explicit AI clause in the policy does more work here than any scan.
There is no standard to copy for this. The National Cyber Security Centre is the only government body publishing dedicated shadow IT guidance, while the National Institute of Standards and Technology has no glossary entry for the term, ISO has no dedicated standard and ITIL does not cover it. What follows is drawn from that guidance and from the parts of a shadow IT policy that survive contact with users.
A policy that only prohibits things gets ignored, because the behavior it targets comes from an unmet need. The useful version defines the approved route as clearly as it defines the boundary, which is the same principle that governs a broader IT Asset Management policy.
A workable shadow IT policy covers these clauses:
Two of those carry most of the weight. The turnaround commitment is what makes the official route competitive with the unofficial one, and the no-blame clause is what gets existing shadow IT declared instead of hidden. A policy that gets neither right will be accurate and unused.
Compliance here is a design problem more than an enforcement one. The National Cyber Security Centre’s own recommendations are mostly organizational: avoid unnecessary lockdowns, put a simple request process in place as quickly as possible, provide controlled access to outside services, and take a no-blame approach to people who were pushed into workarounds.
The practical test is speed. If a sanctioned tool takes three weeks to approve and a corporate card takes ninety seconds, the policy is competing on the one dimension it cannot win, and building a culture of cybersecurity around it will not change that arithmetic. Publishing the turnaround alongside the prohibition is what changes it.
Discovery produces a list, and the list is not the outcome. Every item on it needs one of four decisions, and which one depends on what the tool does, what data it touches and how many people already rely on it. Working through them item by item is what converts a detection exercise into managed inventory.
Each finding resolves into one of these outcomes:
The criteria that decide between them stay consistent: sensitivity of the data involved, whether an existing contract already covers the capability, the compliance exposure it creates, the number of active users, and whether a sanctioned alternative exists at all. Anything sanctioned has to land in the IT asset inventory with a named owner, or it becomes shadow IT again as soon as the person who introduced it changes role. Setting a review date on the record is what prevents that.
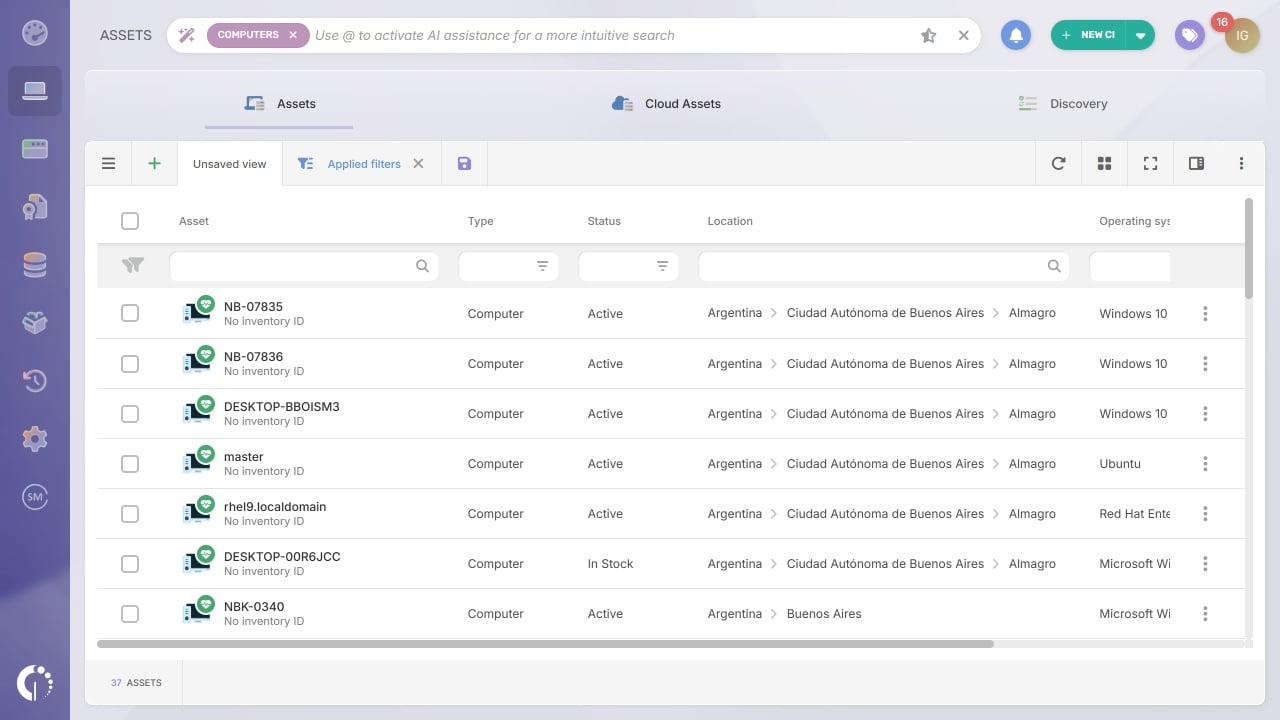 InvGate Asset Management discovers and manages hardware, software and cloud assets in one interface, with no-code automation and lifecycle tracking from acquisition through to disposal. It runs in the cloud or on your own infrastructure, including air-gapped environments, with the same functionality either way.
For shadow IT specifically, every pass described above lands in the same inventory. Network scans and endpoint reporting populate it, software classification turns it into a queue of findings, and automations act on that queue without anyone having to watch it.
Five capabilities do most of the work, and the shadow IT detection tour shows how each one is configured:
Connect our solutions with the apps you use every day.
Explore InvGate's integrations
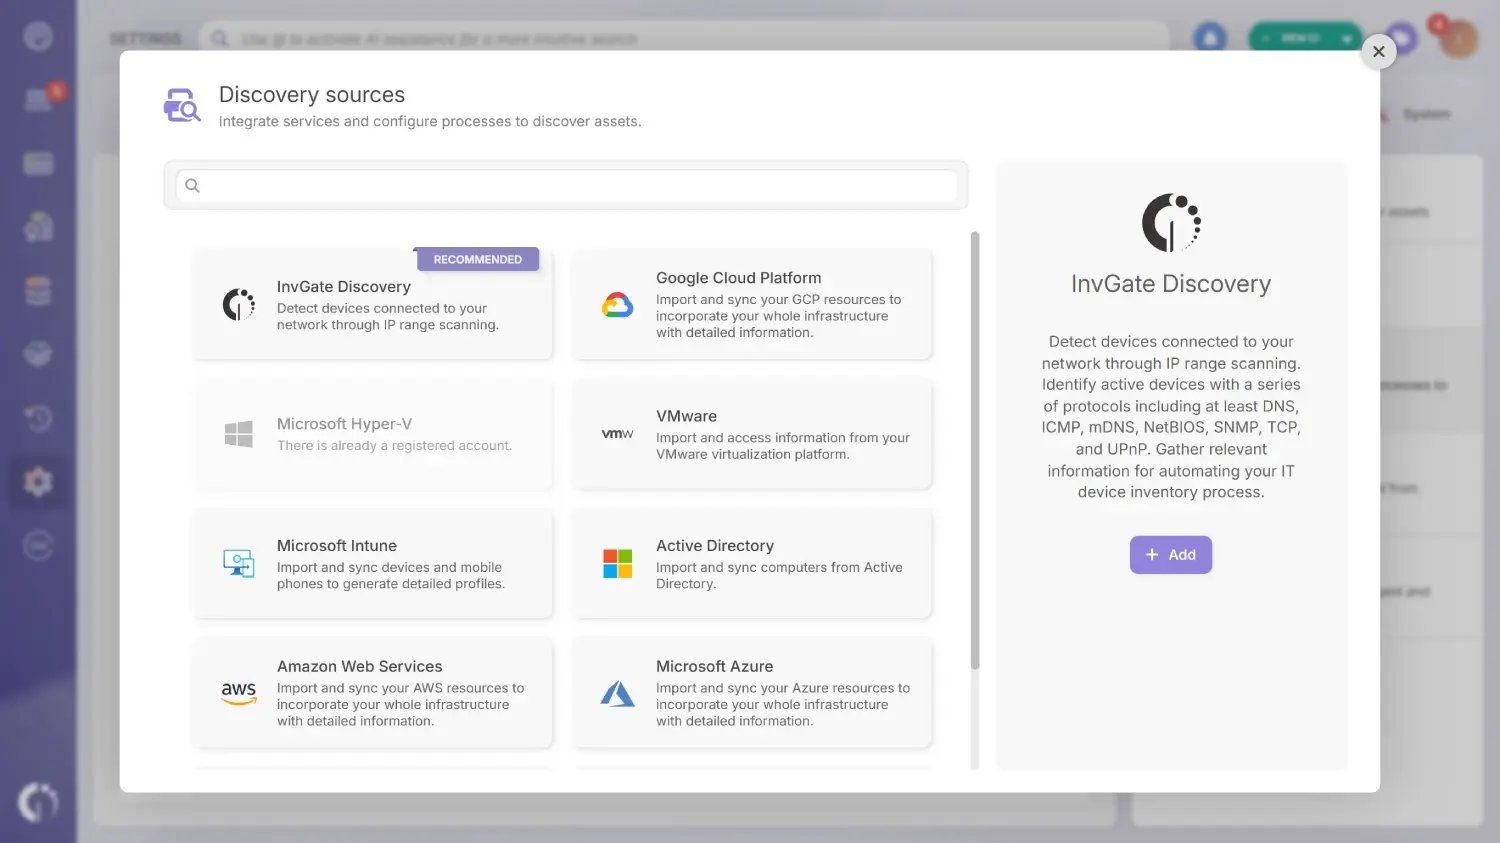 The hardware side starts with a network scan and ends with a decision about each device that answers. The whole sequence takes five steps:
What is left in Assets > Discovery after step 4 is the hardware side of your shadow IT list. Each entry goes to one of the four decisions in the previous section, and the Smart Tag from step 5 is what stops the list rebuilding quietly.
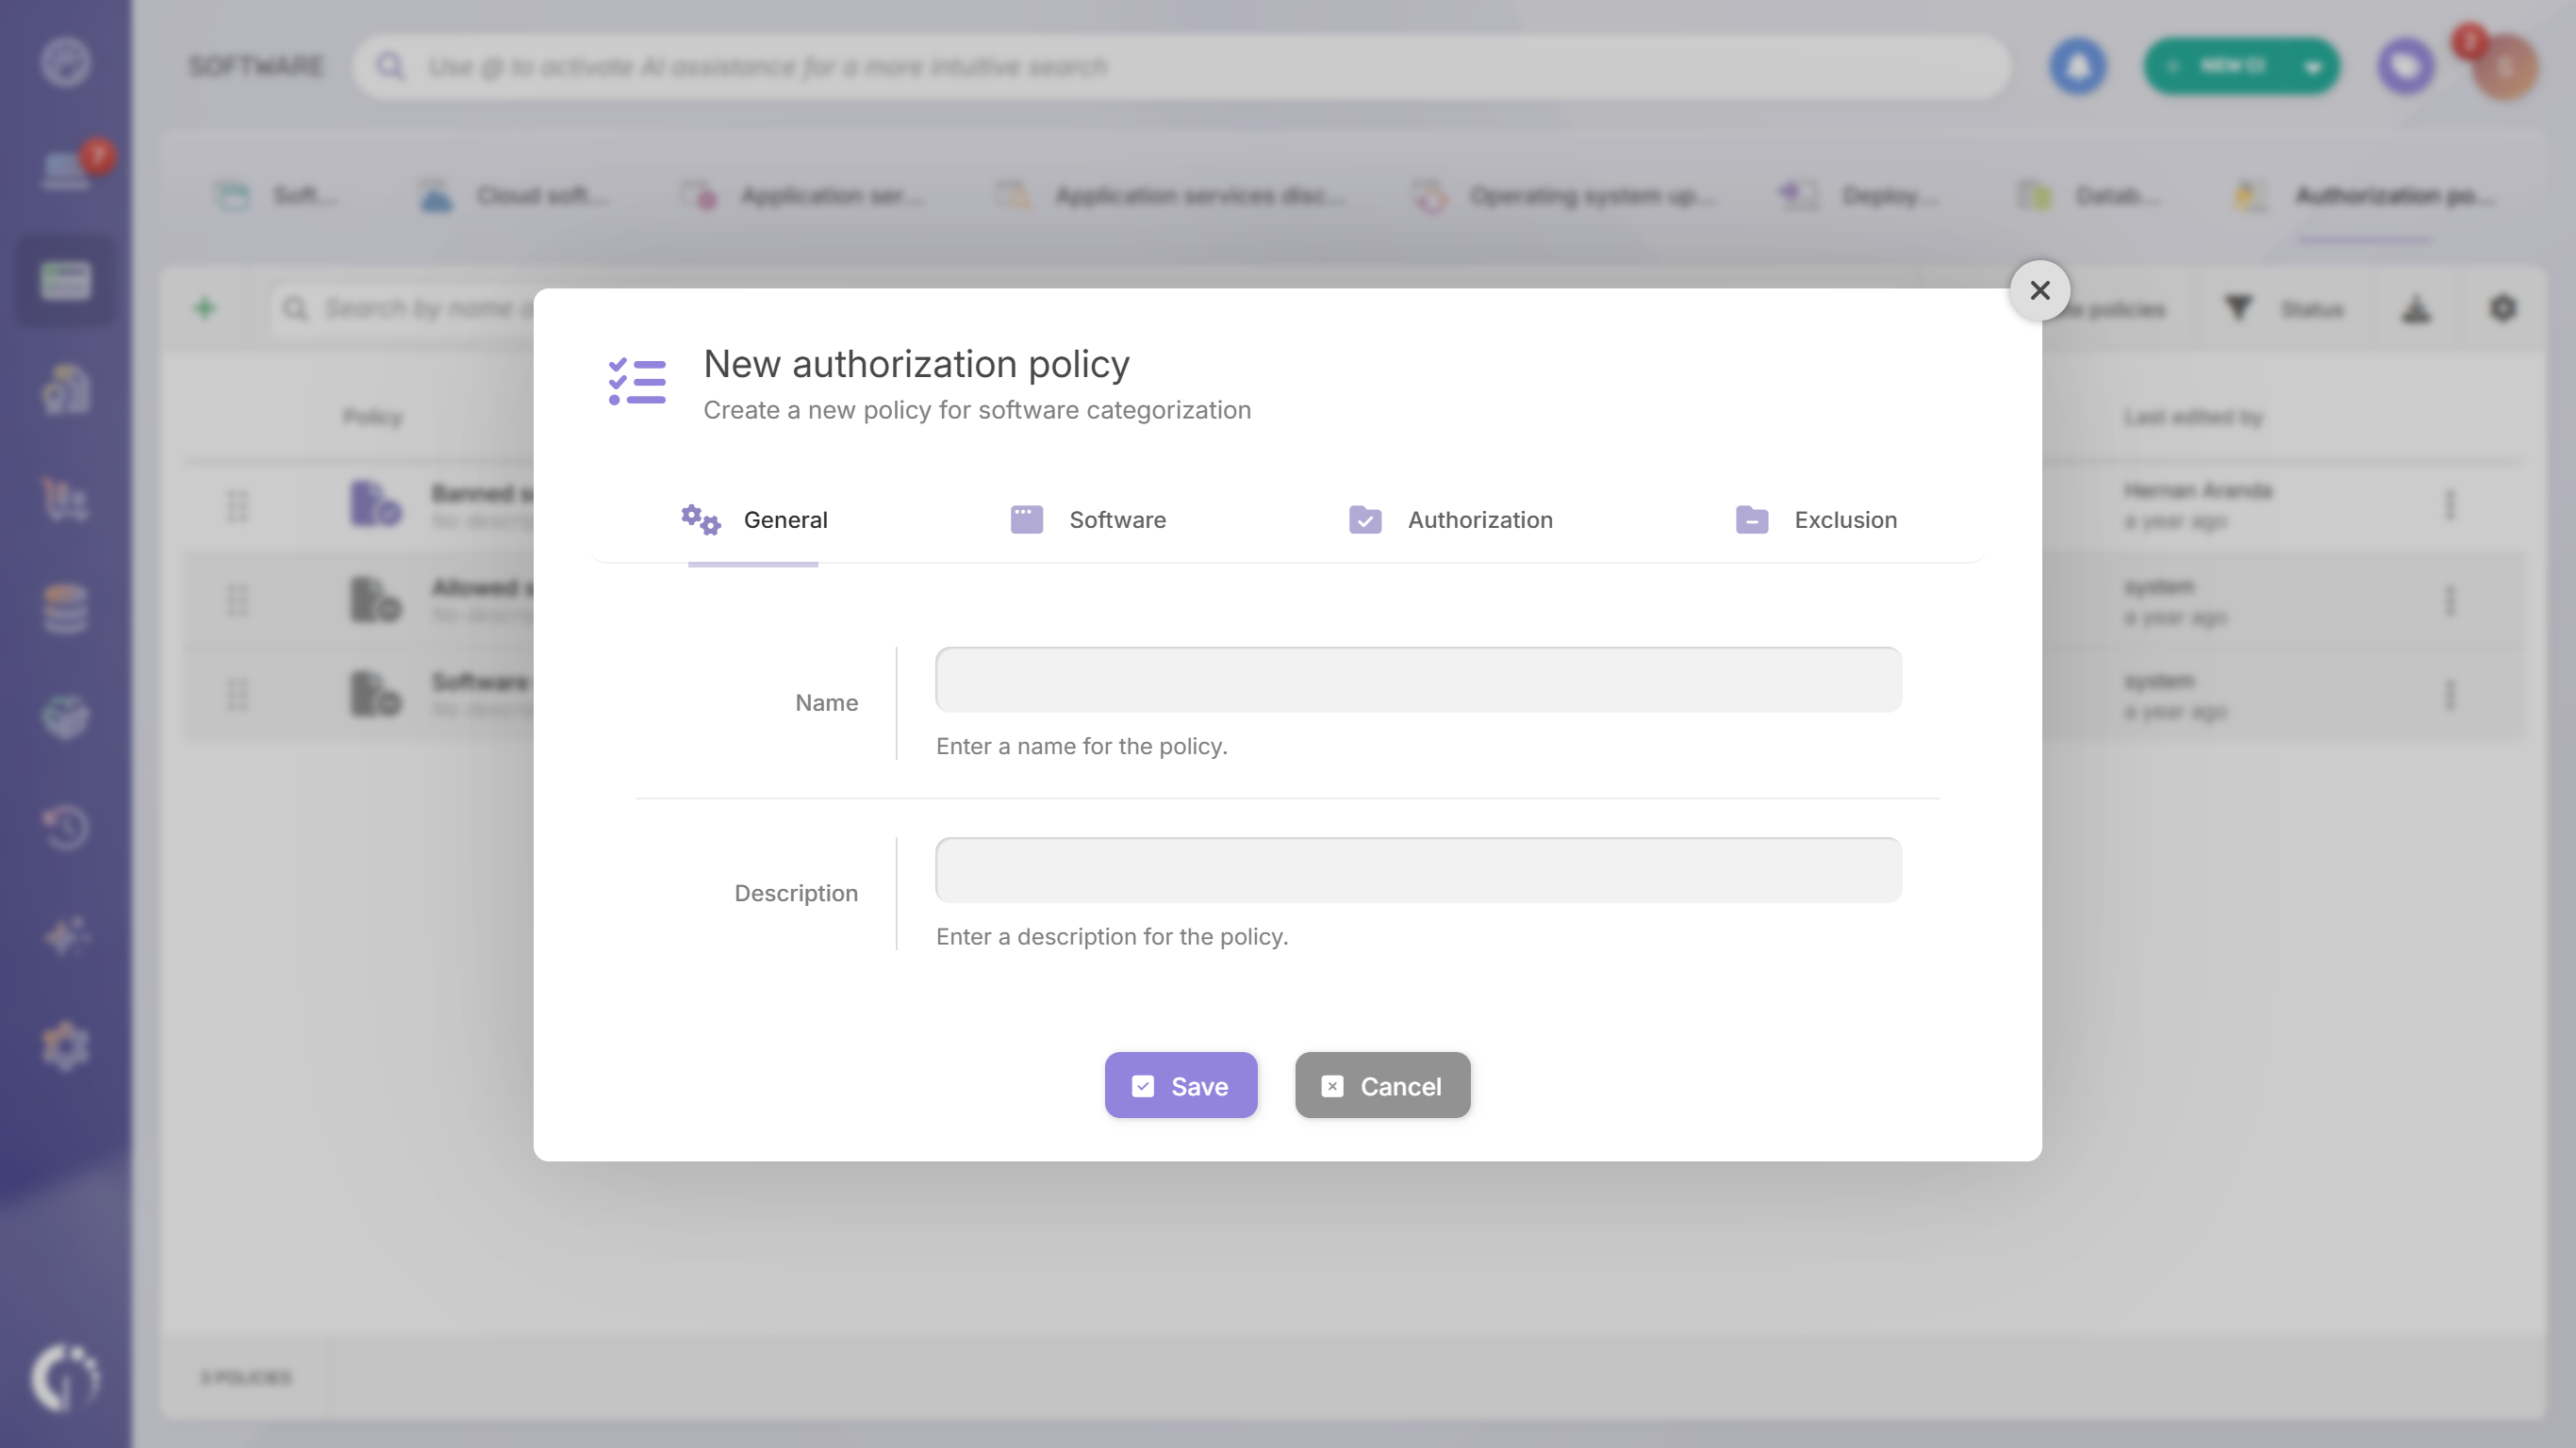 This side runs on the Agent, so deploy it first from Settings > Discovery > Agent Deployment, choosing the OS of the target assets and either manual or remote installation through a Group Policy Object. Once endpoints are reporting every installed title, four steps take you from a written policy to a clean fleet:
Two mechanics matter once you run more than one policy: they are evaluated in list order, so an exception has to sit above the general rule it modifies, and an automated uninstall is configured one title at a time, which suits the applications that genuinely cannot stay rather than a whole prohibited category.
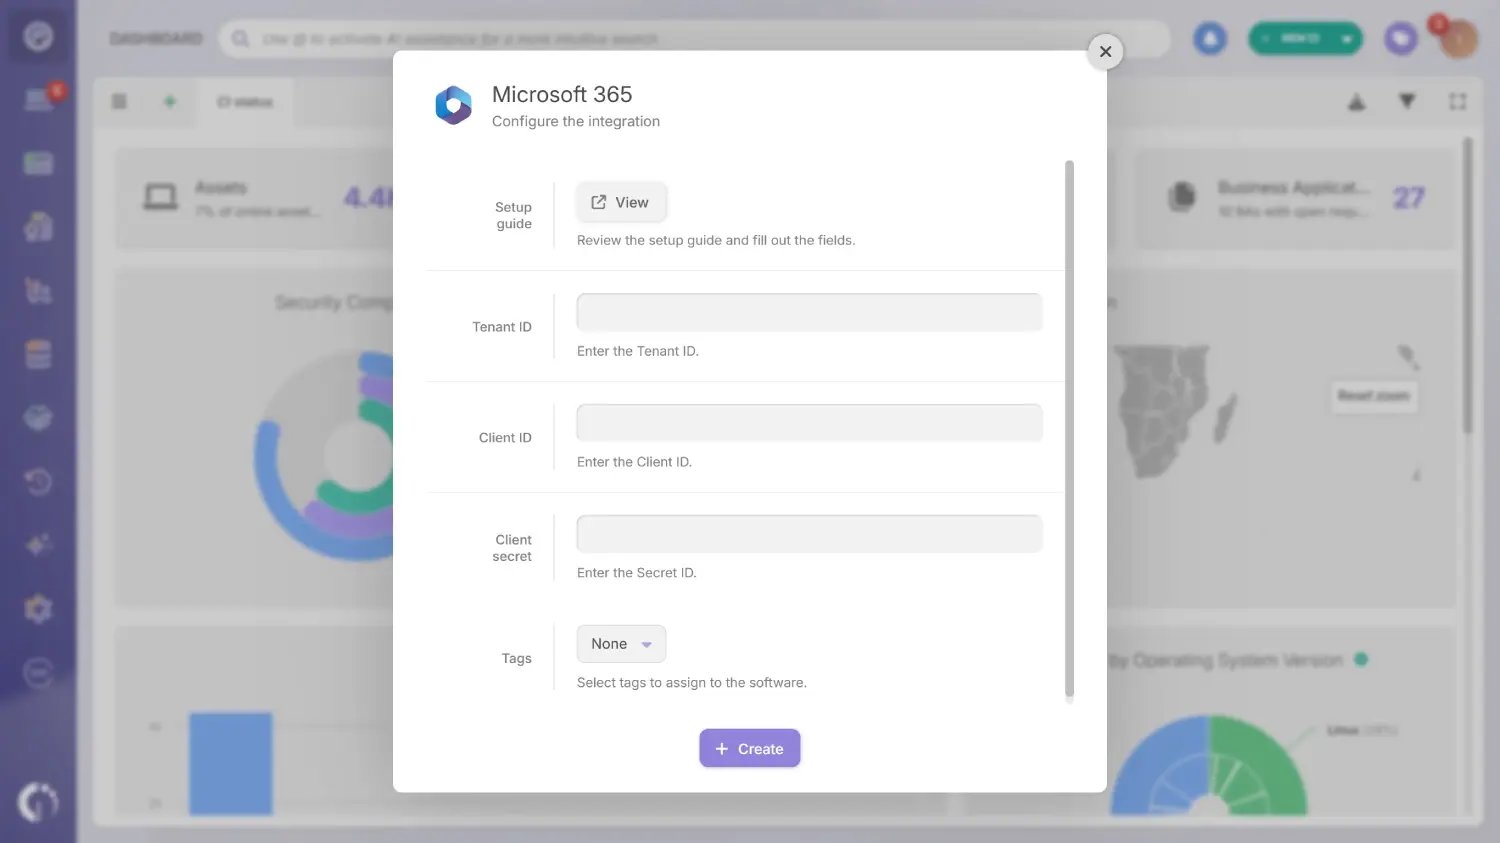 Neither of the passes above sees a subscription that was bought with a card and never installed anything. Three steps close that side:
This is the pass that turns duplicate spending into something you can cancel rather than something you suspect. It is also the one that most often produces the argument for sanctioning a tool instead of blocking it, because the user count is right there.
Setting this up takes less time than the first sweep usually does. You can start a free trial for 30 days, or talk to Sales about how the detection and policy workflow would fit your environment.
Shadow IT will keep appearing for as long as people have work to do and the official route is slower than a corporate card. The workable objective is a known list, where everything running is identified, owned, and either sanctioned or scheduled for removal.
Detection from the asset inventory produces that list, a policy with a published turnaround keeps it from growing back, and a per-item decision framework converts it into managed inventory. That sequence is how to manage shadow IT without slowing down the teams who created it in the first place.
Shadow IT raises the same handful of questions in most organizations. The answers below follow the definitions and sources used throughout this article.
Shadow IT is not bad by definition. The risk comes from the asset being unknown rather than from the tool itself, which is why the National Cyber Security Centre describes shadow IT as an unmanaged risk. The same application becomes acceptable as soon as it has an owner, a contract and an inventory record.
The recurring categories are file sharing and storage services, messaging and collaboration tools, project trackers, design tools and, increasingly, generative AI assistants. What they share is that one person can adopt any of them in a browser with no help from IT. Categories that need installation or procurement appear far less often.
Gartner reported in 2023 that 41% of employees had acquired, modified or created technology outside IT’s visibility during 2022, and predicted that share would reach 75% by 2027. On unsanctioned AI specifically, Gartner reported in November 2025 that 69% of organizations suspect or have evidence that employees are using prohibited public generative AI, from a survey of 302 cybersecurity leaders. Figures on this topic vary widely between publishers, so it is worth checking the sample behind any number before repeating it.
Cloud services are what made shadow IT trivial to create. A subscription can be started with an email address and a card, with no installation, no procurement and no network artifact for a scan to find. That is why shadow IT detection has to cover subscription records and identity logs alongside device scans.

