Software Audit: Types, Process, And an 18-Point Checklist (2027)

Software Audit: Types, Process, And an 18-Point Checklist (2027)

Join IT Pulse

Receive the latest news of the IT world once per week.

A software audit is a formal review of how an organization uses and manages its software licenses. In its simplest form, it checks if the software you run is legal, properly licensed, and aligned with all compliance requirements.

Most IT teams find out where they stand only when a vendor's audit letter arrives, and by then the spreadsheets are months out of date. This guide covers the types of software audit, what triggers one, the software audit process, and an 18-point checklist to run your own review first.

What is a software audit?

A software audit is a structured review of an organization's software environment to verify that applications are properly licensed, secure, and aligned with compliance requirements. It typically includes taking inventory of installed software, validating licenses, comparing usage against entitlements, and identifying risks like unauthorized apps or outdated versions. This guide covers its meaning in IT Asset Management (ITAM); in software development, the same term also names a review of source code quality or security.

This process can be done manually with spreadsheets and checklists, but most organizations rely on tools to automate discovery, reporting, and compliance checks. Modern solutions even allow audits to run periodically and automatically, which keeps oversight continuous between vendor reviews and annual checkups.

Why do you need to audit software?

The main reason to perform software audits is to make sure your organization stays compliant with all requirements while avoiding unnecessary risks and costs. Every installation without a matching license, and every application nobody approved, is a liability that grows until someone finds it.

Regular audits put your team in control of the software environment. Fines, disruptions, and shadow IT surface on your schedule, with time to fix them before an external review does. Those regular reviews pay off in six ways:

  • Ensure compliance: verify that all software aligns with vendor agreements, internal policies, and industry regulations.
  • Reduce financial risk: avoid unexpected penalties, fines, or costly true-ups during external audits.
  • Optimize license usage: find underused or unused licenses and reclaim them through license harvesting.
  • Strengthen security: detect unauthorized or outdated applications that could expose vulnerabilities.
  • Improve governance: keep a clear chain of custody and reports that support IT governance and decision-making.
  • Increase efficiency: automate repetitive audit tasks, saving time and reducing human error.

Types of software audit

Not every software audit looks the same. Depending on who performs it and why, the scope and focus can vary, and knowing the difference helps organizations prepare properly and avoid surprises.

The table below sums up the main types, who runs each one, and when it makes sense:

Type Who performs it What it checks When it applies
Internal audit Your IT, ITAM, or Software Asset Management (SAM) team Installations against licenses, unauthorized software, outdated versions On a set schedule, and before renewals or expected vendor reviews
Vendor hard audit The software publisher or an audit firm it appoints License compliance against the terms of your contract When the publisher invokes the audit clause in your license agreement
Vendor soft audit The software publisher or one of its partners Deployment and usage data you agree to share When the publisher proposes a voluntary license review
Regulatory audit External auditors or regulators How software that handles sensitive data meets frameworks like the General Data Protection Regulation (GDPR), the Health Insurance Portability and Accountability Act (HIPAA), or the Sarbanes-Oxley Act (SOX) When your industry or jurisdiction requires it
Independent audit A third-party firm the organization hires An objective view of your compliance position Before a vendor audit, during mergers and acquisitions, or to validate internal findings


Internal and independent audits are the ones you schedule yourself. The other three come from outside, and how prepared your data is decides how much they cost you.

Hard audits vs. soft audits

A hard audit is the formal review a publisher launches under the audit clause of your license agreement. It is binding, it follows the notice period the contract sets, and its findings turn into true-up invoices or penalties. A soft audit, often called a license review or license assessment, asks you to share deployment data voluntarily, and Microsoft, for example, offers Software Asset Management engagements through its partners.

A soft audit can be declined or scoped, so before agreeing to one, check what data you'll share and whether the review is tied to a renewal or a sales proposal. A hard audit notice calls for a different playbook: gather proof of entitlement, reconcile installations against it, and fix gaps before the auditors arrive, as covered in our software license audit guide.

What triggers a software audit?

A software audit can be triggered by several factors, some within your control and others imposed by external parties. Understanding these triggers helps organizations anticipate audits and build a solid software audit defense:

  1. Vendor suspicion or red flags: software vendors may launch an audit if they detect unusual license activity, usage patterns that don't match purchased entitlements, or if they suspect unlicensed deployments.
  2. Contractual obligations: many license agreements explicitly grant vendors the right to perform periodic audits, meaning an audit can be scheduled even without suspicion.
  3. Regulatory requirements: in industries like healthcare, finance, or government, compliance frameworks (for example, GDPR, HIPAA, or SOX) can trigger audits to ensure that software handling meets industry standards.
  4. Mergers and acquisitions: during due diligence, acquiring companies often conduct software audits to confirm compliance and avoid inheriting risks.
  5. Internal governance: organizations may initiate their own audits as part of IT Asset Management practices, either on a set schedule or in preparation for a potential vendor or regulatory audit.
  6. Security incidents: a data breach or the discovery of unauthorized software can prompt a targeted audit to identify vulnerabilities and confirm compliance.
  7. Poor compliance history: if a company has previously failed audits or struggled with software audit compliance, vendors are more likely to re-audit to verify corrective actions.
  8. Third-party reports: BSA, The Software Alliance, runs a public form to report unlicensed software use, and those reports are one of the ways publishers learn about suspected under-licensing.

Several of these triggers sit outside your control. What you control is how current your software data is when one of them arrives.

How to do a software audit? The software audit process

A software audit is closely related to any other IT audit but with a narrower scope. IT audits evaluate the entire technology landscape, from systems and networks to data and controls, while a software audit focuses specifically on applications and the goal of keeping them licensed, compliant, and free from unnecessary risks.

The software audit process follows a series of structured steps, many of which mirror those of an IT audit (you can find the full breakdown in our IT audit guide):

  1. Planning: define the scope, objectives, and resources of the audit.
  2. Inventory and data collection: identify all installed applications across your environment.
  3. License and compliance review: compare actual usage against entitlements, contracts, and compliance requirements to establish your effective license position.
  4. Risk assessment: flag unauthorized or outdated software and assess their impact.
  5. Testing and validation: verify findings through document reviews, interviews, and audit tools.
  6. Analysis and evaluation: consolidate results to identify gaps, redundancies, or compliance issues.
  7. Reporting: produce a software audit report with findings, risks, and recommendations.
  8. Follow-up: implement corrective actions and set controls for ongoing compliance.

Steps 2 and 3 take the most time in a manual audit, because they depend on data scattered across devices, contracts, and invoices. They are also the steps a software audit tool automates first.

18-point software audit checklist

The process above describes the stages of a software audit. This software audit checklist breaks them into 18 items you can tick off as you go, grouped into six phases, to confirm that every piece of software in your environment is properly licensed, compliant, and secure.

#1: Planning

  • Define the audit scope (systems, departments, or vendors).
  • Set clear objectives (compliance, cost optimization, risk reduction).
  • Assign responsibilities and gather the right audit team.

#2: Data collection

  • Use discovery tools to create a complete software inventory.
  • Gather purchase records, license agreements, and entitlements.
  • Document software versions, installations, and usage data.

#3: Compliance review

  • Match installed software against licenses and entitlements.
  • Check alignment with vendor agreements, internal policies, and industry regulations.
  • Identify unauthorized or shadow IT applications.

#4: Risk and usage assessment

  • Flag outdated or unsupported software that could introduce vulnerabilities.
  • Analyze usage to spot underutilized or unused licenses.
  • Assess the potential financial and security risks.

#5: Verification and reporting

  • Cross-check data and interview key stakeholders if needed.
  • Prepare a software audit report summarizing gaps, risks, and recommendations.
  • Share findings with leadership and stakeholders.

#6: Remediation and follow-up

  • Take corrective actions to resolve compliance gaps.
  • Update internal policies and controls.
  • Establish periodic, automated audits with a software auditing tool to maintain continuous compliance.

How to adapt our IT audit checklist to a software audit

A software audit is usually one piece of a broader IT audit, so we also offer a downloadable IT audit checklist that covers the full environment. It contains a five-stage process checklist, with space for the people involved and a due date on each item, and a question checklist across 15 areas, from network security to disaster recovery.

For a software audit, use the process checklist as your calendar and keep the question areas that touch software:

  • Application security.
  • System Patch Management.
  • Compliance.
  • Vendor Management.
  • Asset Management.
  • Cloud security.

The downloadable does not include license items, so add the compliance and usage points from the 18-point checklist above. The result is one working document that covers the software side in depth and still fits inside a wider IT audit.

Software audit examples

Sometimes definitions can feel abstract, so let's ground this topic with a few real-world examples of software audits. These scenarios show the different situations where audits take place and what they typically uncover:

  • Internal license compliance check: an organization's IT Asset Management team performs an internal software audit using a discovery tool to confirm that all Microsoft 365 licenses are assigned correctly and that no unapproved copies are installed.

  • Vendor-driven audit: Oracle initiates an external software audit after noticing unusual usage patterns in a client's database environment. The audit reveals several under-licensed deployments that require a costly true-up.

  • Vendor soft audit: a publisher offers a free license review ahead of a renewal. The data the company shares ends up supporting a proposal to move to a larger subscription tier.

  • Regulatory audit in healthcare: a hospital undergoes a software audit as part of a broader HIPAA compliance check. Auditors review all applications handling patient data to ensure they are licensed, updated, and properly secured.

  • Mergers and acquisitions due diligence: during an acquisition, the buyer conducts a software audit on the target company's systems. The process uncovers several shadow IT applications without proper licenses, which are flagged as financial and legal risks.

  • Security-triggered audit: after a ransomware incident, a financial services company runs an urgent internal software audit to detect outdated or unsupported applications that may have been the entry point for attackers.

In every case, the cost of the audit depends on how much of the data was already collected when it started. Teams with a current inventory go straight to the findings and skip the rebuild.

Software audit tools: what to look for

Software audit tools replace the spreadsheets that make manual audits slow and error-prone. Whatever the tool, it should cover four jobs:

  • Automatic inventory: detect installed software on every device and keep the list updated without manual imports.
  • Installations against licenses: cross-check what is installed with what the contracts allow, and show the gap in units and cost.
  • Authorization policies: classify software as allowed or prohibited and flag installations that break the rules.
  • Auditor-ready reports: produce the evidence an auditor asks for without rebuilding it for every review.

Most IT Asset Management software covers some of these jobs, and our roundup of IT audit software compares how deep each platform goes. Checking those four jobs during a free trial is the fastest way to tell the options apart.
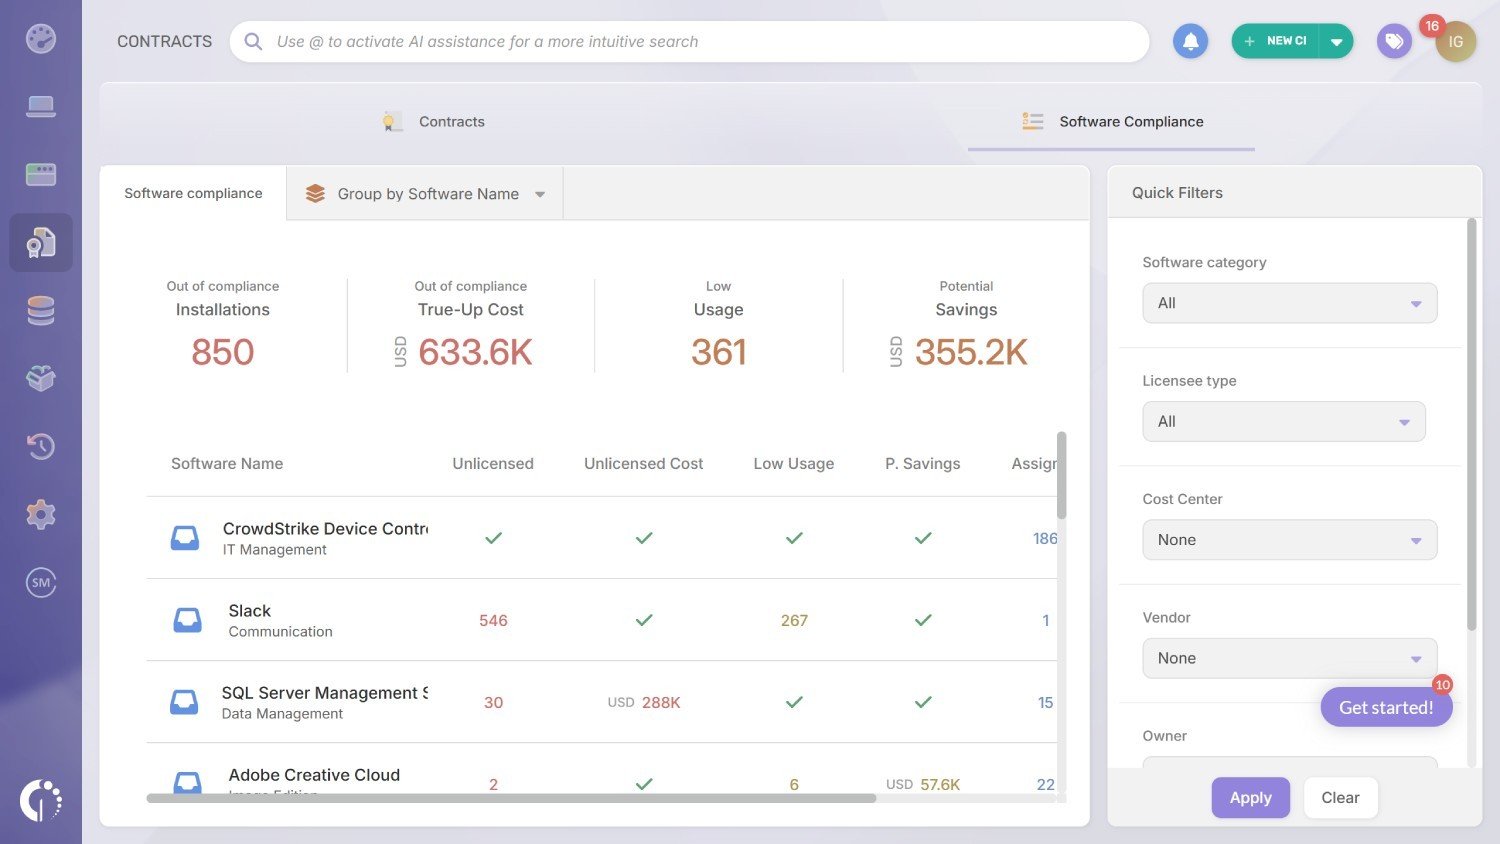
Using InvGate Asset Management as your software audit tool

invgate-asset-management-software-compliance-module-screenshotInvGate Asset Management brings hardware, software, and cloud assets into a single interface, with no-code automations and a choice of cloud or on-premises deployment. Its pricing is transparent and published, so teams can size the investment before they talk to anyone.

For a software audit, the platform keeps both sides of the comparison in one place. Entitlements live in contract records, the InvGate Agent collects installations and usage from each device, and the Software Compliance module sets one against the other, so the data is already assembled when a vendor asks for it.

InvGate Asset Management key features for software audits

These are the capabilities that cover each stage of the audit, from the inventory to the report you hand over:

  1. Software inventory and metering: the Agent records the software installed on each device, with its version, and Software Metering tracks how often each application is used.
  2. Software contracts and license assignment: record what you bought in each software contract and assign every license to its licensee, so entitlements sit next to the installations they cover.
  3. Software Compliance module: under Contracts > Software Compliance, see out-of-compliance installations, out-of-compliance true-up cost, low usage, and potential savings, filtered by software category, licensee type, cost center, or provider.
  4. Authorization policies: classify titles as allowed, under review, or prohibited and flag installations that break the policy (Professional and Enterprise plans). Remove them with the Uninstall software action or a scheduled automation.
  5. Reports, dashboards, and Smart Recommendations: schedule reports and build dashboards for auditors, while Smart Recommendations flags issues like unassigned licenses with the action to fix them.

Ready to simplify your next software audit? Start your free 30-day trial of InvGate Asset Management or talk to Sales to see how it fits your environment.

Do you need a software audit certification?

When it comes to software audits, there isn't a single, universal certification required to perform one. Internal IT teams, consultants, or vendor representatives can all carry out audits without needing to be licensed auditors.

However, there are certifications and frameworks that add credibility and structure, and our guide to IT Asset Management certifications compares them in depth. These are the ones most tied to software audits:

  • SAM certifications: the International Association of IT Asset Managers (IAITAM) offers the Certified Software Asset Manager (CSAM) and Certified IT Asset Manager (CITAM), which build expertise in software lifecycle management and audit readiness.
  • ISO/IEC standards: ISO/IEC 19770-1:2017 sets the requirements for an IT Asset Management system, and organizations align with it to show the maturity of their SAM practice.
  • Audit and compliance certifications: ISACA offers the Certified Information Systems Auditor (CISA) and Certified in Risk and Information Systems Control (CRISC) credentials, often held by professionals who run regulatory or IT audits that include software.

Do you need them?

Whether a certification matters depends on who runs the audit. Here is how it breaks down:

  • For internal audits: no certification is required, but trained staff or certified SAM professionals make the process more reliable.
  • For external or vendor audits: vendors perform them with their own auditors, and the organizations being audited need no certification.
  • For consultants and third parties: certifications add credibility, especially when they offer audit services to clients.

In short, certifications strengthen a SAM program, and none of them is required to run a software audit. What an audit does require is accurate data and a repeatable process.

In conclusion

A software audit tells you whether the software you run matches what you are entitled to use, and whether it is authorized and supported. Knowing the difference between internal, hard, and soft audits helps you decide which ones to schedule, which ones to negotiate, and which ones to prepare for.

The teams that go through audits calmly are the ones that run them before anyone asks. With a clear process, an 18-point checklist, and a tool that keeps inventory and contracts connected, the next software audit becomes a routine review.

Frequently asked questions

These are the questions that come up most often when teams prepare their first software audit. Each answer summarizes what the sections above cover in more detail.

What is a software audit?

A software audit is a formal review that checks whether the software an organization runs is properly licensed, authorized, and supported. It can be run internally or requested by a vendor, a regulator, or an independent auditor.

How often should you audit software?

Most organizations run an internal software audit at least once a year and review their highest-risk publishers more often, for example before each renewal. With automated inventory and compliance tracking, the review can run monthly or quarterly with little extra effort.

What happens if you fail a software audit?

Failing a vendor software audit usually means buying the missing licenses and paying any back-maintenance or penalties the contract allows. Internal audit findings carry no penalty, since they give the team a list of gaps to fix before an external review.

Who performs a software audit?

Internal audits are run by the IT, ITAM, or SAM team, sometimes with support from finance and legal. External audits are run by the software publisher, an audit firm it appoints, a regulator, or an independent third party the organization hires.

Simplify your IT ecosystem with InvGate Asset Management

30-day free trial - No credit card needed

Clear pricing

No surprises, no hidden fees — just clear, upfront pricing that fits your needs.

View Pricing

Easy migration

Our team ensures your transition to InvGate is fast, smooth, and hassle-free.

View Customer Experience