InvGate Service Management connects to Active Directory and Microsoft Entra ID (formerly Azure Active Directory) to centralize how your organization manages user accounts and sign-in. The Active Directory connection synchronizes users and groups into your instance, while Entra ID handles authentication through SAML single sign-on.
Workflows can also act on Entra ID directly, creating, enabling, or disabling accounts as part of a request. This guide covers configuring each part: the directory sync, SAML sign-in, and automating user provisioning for onboarding and offboarding.
Why do you need to integrate InvGate Service Management and Active Directory?
Connecting the two tools solves several recurring User Management problems:
- Richer user records — Active Directory attributes like job title, department, and contact information surface in InvGate Service Management, giving agents context during ticket resolution.
- Faster setup — you can import a large number of users and accounts from your directory in a single synchronization rather than creating them by hand.
- Consistent data — user information stays aligned across both systems as the directory changes.
- Simpler sign-in — people log in with their existing Active Directory or Entra ID credentials through single sign-on.
- Automated onboarding and offboarding — workflows can create, enable, or disable Entra ID accounts directly, so joiner and leaver requests provision and revoke access without manual steps.
If your team also manages hardware and software, you can bring the same directory into InvGate Asset Management through its own Active Directory connection.
Prerequisites for the InvGate Service Management-Active Directory integration
Before you start, gather the configuration data for each side.
For the Active Directory synchronization, you need the hostname or IP address of your Active Directory server, the directory domain, and the domain name, plus an administrator account with read access to the directory.
For Entra ID single sign-on, you need access to the Microsoft Entra admin center (or Azure portal) with permission to create an enterprise application, along with the SAML values it generates: the Entra identifier, the login URL, and the Base64 certificate. You enter these on the InvGate Service Management side, so administrator access there is required as well.
How to integrate InvGate Service Management with Active Directory and Azure
The setup has two phases: synchronizing user data from Active Directory, and configuring Entra ID for authentication through SAML single sign-on.
Integrating InvGate Service Management with Active Directory
- Go to Directory Services. In InvGate Service Management, navigate to Settings > Users > Directory Services.
- Add the configuration. Click Add to open the LDAP configuration screen.
- Complete your Active Directory details. When you fill in the Domain, the Domain Name and Base DN fields complete automatically.
- Set your options. The Options section lets you customize the configuration:
- Import on the fly — add users to InvGate Service Management automatically the first time they log in with their LDAP credentials.
- Allow user search — search for and import users directly while creating a request on their behalf.
- Import groups — bring in the groups associated with your LDAP users.
- Import OUs — bring in the organizational units associated with your LDAP users.
- Import managers — bring in the manager associated with your LDAP users.
- Sync — set how often Active Directory and InvGate Service Management synchronize.
- Import and map. Once the configuration is saved, use the import buttons to bring in users and groups, and the Change field matching button to choose which fields are filled from Active Directory.
Integrating InvGate Service Management with Microsoft Entra ID (SAML single sign-on)
- Create the enterprise application. In the Microsoft Entra admin center (or Azure portal), go to Enterprise applications, then Create your own application. Give it a name and choose "Integrate any other application you don't find in the gallery." Select SAML as the sign-on method.
- Configure the SAML settings. Edit the basic SAML configuration:
- Identifier (Entity ID) — the URL of your InvGate Service Management.
- Reply URL (Assertion Consumer Service URL) — your InvGate Service Management SAML endpoint (for example,
https://URL_Service_Management/saml).
- Complete the configuration in InvGate Service Management. Go to Settings > Users > Authentication and open the SAML service under Authentication services. Add users and groups to the application in Entra ID if your portal requires it, then enter the values Entra ID provides — the identifier, the Login URL, and the Base64 certificate — in the Entity ID, Login URL, and Certificate fields. Upload the certificate as Public Key (PEM by default, or use the All files option for the format Entra ID provides). Save, then enable the connection, and confirm it by signing out and back in with the SAML button.
To end a user's InvGate Service Management session and their identity-provider session together, enable SAML Single Logout as part of the same configuration. Signing out of InvGate Service Management then also signs the user out at Entra ID, which matters on shared devices and during access reviews.
Automate onboarding and offboarding with Microsoft Entra ID
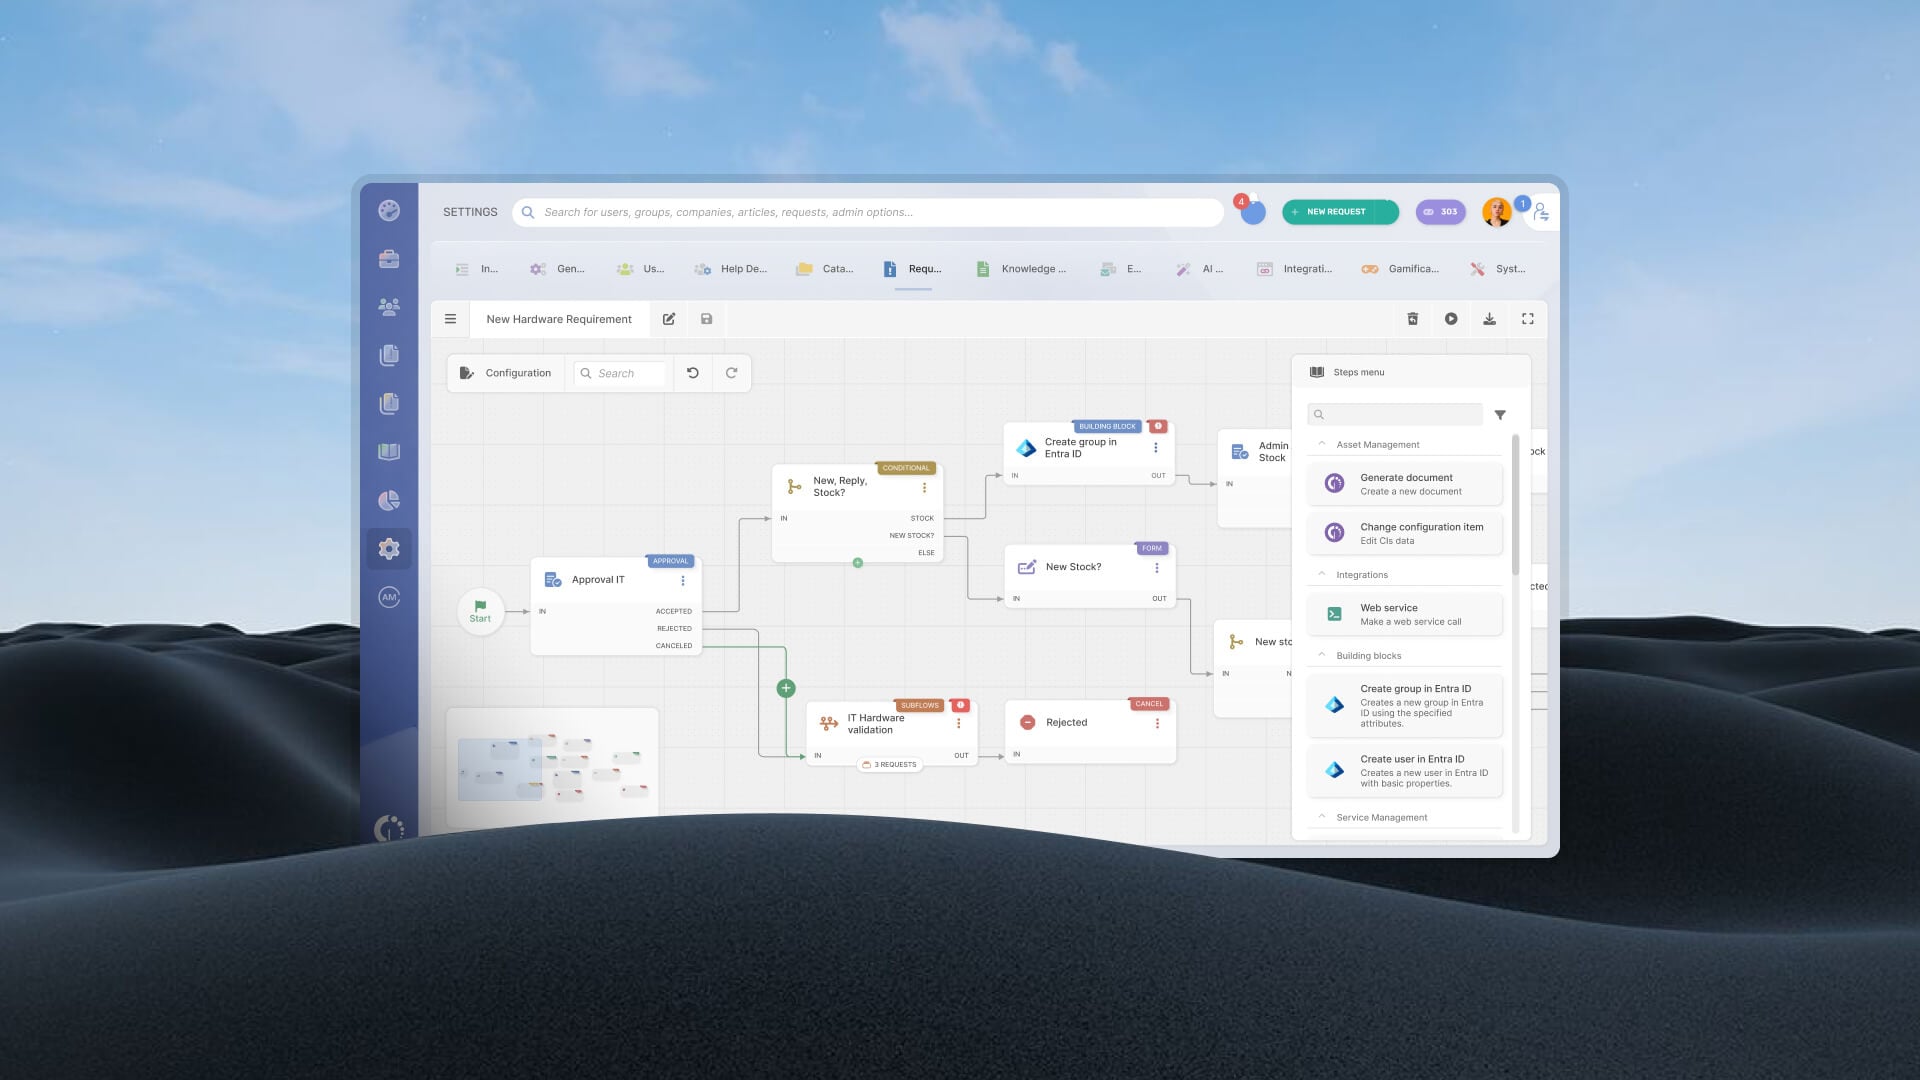
Beyond syncing users and handling sign-in, InvGate Service Management can act on Entra ID from inside a request. Its no-code workflow builder includes Built-in Action Connectors: pre-configured Entra ID actions that run as workflow steps without custom web services or API scripting. These cover creating users and groups, editing user profiles and settings, enabling and disabling users, assigning temporary passwords, reading user and group data, and removing groups.
Some practical examples of how to use these are common HR workflows:
-
Onboarding. When a new-hire request comes in, a workflow can create the person's Entra ID account with the create-user block, assign a temporary password they reset at first sign-in, and add them to the right groups, so their access is ready before day one.
-
Offboarding. When someone leaves, a leaver request can disable their Entra ID account to cut off access immediately, then adjust their group memberships, without an administrator editing the directory by hand.
Next steps
With the directory connected, a few steps help you get the most out of InvGate Service Management:
- Assign roles and permissions so administrators, managers, agents, and end users each have the right level of access.
- Set up your help desks to organize support areas and route tickets to the right teams.
- Build your service catalog so each service carries its routing, escalations, and SLAs.
Connecting Active Directory and Microsoft Entra ID turns user provisioning and sign-in into something your service desk manages centrally, with less manual work and tighter access control. If you'd like help mapping the integration to your directory setup, talk to our team, or start a 30-day free trial to set it up in your own instance.
Active Directory integration FAQ
Does InvGate Service Management integrate with Microsoft Entra ID?
Yes. It connects to Entra ID (formerly Azure Active Directory) for SAML single sign-on, and workflows can act on Entra ID directly to manage accounts.
Can users log in with their Active Directory credentials?
Yes. Once single sign-on is configured, people sign in to InvGate Service Management with their existing Active Directory or Entra ID credentials.
Can InvGate Service Management create or disable users in Entra ID?
Yes. Built-in Action Connectors let workflows create, enable, disable, and update Entra ID users and groups as part of a request.