




Most IT teams can name the laptops they handed out and the servers they racked. The gap shows up everywhere else: the switch someone added to a branch office, the printer that arrived with a department, the test machine that was never decommissioned. Network discovery is how that gap gets closed, by scanning the network on a schedule and reporting what answered.
Windows ships a setting with the same name, and that one controls whether a computer shows up to others on a local network. This article covers the IT Asset Management (ITAM) practice: how a scan finds devices, what it can and cannot tell you about them, how agent based and agentless methods divide the work, and how to run a scan and turn the results into inventory.
Network discovery is the automated process of finding devices that are reachable on a network and collecting whatever they will report about themselves. A tool contacts every Internet Protocol (IP) address in a defined range, identifies which ones are active, and records what each one returned.
The scan reaches anything that holds an address and answers, and its particular value is covering the hardware no software agent will ever run on. It is one input into a broader asset discovery strategy, and a single pass over a corporate network typically returns:
A quick clarification before going further: everything in this article refers to scanning a network to build an asset inventory. The identically named Windows option is a separate, per machine setting that controls whether a single computer is visible to others on a local network.
A finished scan hands back a table of devices and the attributes each one exposed over the network. How much arrives depends on which protocols are enabled and whether read credentials are configured, so the same device can come back rich or thin. The fields collected are:
That is enough to know what is on the network, and an Asset Management Database (AMDB) asks for a little more. The fundamentals it rests on are the ones a scan has no way to read: who owns the device, where exactly it sits, what it cost and how it was acquired, its warranty, its lifecycle stage, and which other elements it depends on. Those get filled in when a discovered device is converted into an asset, which is where the rest of this article goes.
The mechanics are consistent across tools. A scanner reaches a range of addresses, speaks a handful of standard protocols to whatever answers, and writes the results somewhere they can be reconciled against records that already exist.
No single protocol sees the whole network, so discovery runs several at once and combines what each returns. Which protocols are enabled decides how much detail comes back, and a device that looks thin in the results is often a device whose protocol was never switched on.
Each protocol contributes something different:
Most tools follow the same five steps, and the quality of the result depends almost entirely on how carefully the first one is done. A range that skips a subnet produces a clean report with a hole in it, and nothing later in the sequence flags the omission.
The sequence runs as follows:
Discovery output only becomes useful once it meets the records a team already keeps. Reconciliation is the step that matches a rediscovered device to its existing entry, updates what changed, and separates the genuinely new from the merely rescanned.
From there the data feeds two places. The asset inventory gains the hardware facts it needs for lifecycle and audit work, and the Configuration Management Database (CMDB) gains the devices and relationships that Change Management depends on when someone needs to know what a planned change will touch.
Network discovery is an agentless method, which means it collects what it can from outside the device with nothing installed on it. An agent takes the opposite approach: a small program runs on the endpoint and reports from the inside, which is how detailed software inventory and usage data get collected at all.
The two cover different ground, and most teams run both, often managed from the same place. For desktops and laptops an agent is the better instrument because it returns more than a scan can, and our breakdown of agent based and agentless approaches goes further into the trade offs.
A scan that completes without errors can still return less than what is on the network. The causes split into two groups, and the first produces results that look like a product fault rather than a configuration problem.
Discovery identifies devices by their MAC address, which makes every failure to read one a device that never reaches the results table. A device sitting in a different subnet than the scanning proxy is the common case, because its MAC cannot be resolved across the boundary.
The other case is Proxy ARP. When a switch, router or access point answers on behalf of certain addresses, every device behind it reports that same MAC, and devices that cannot be told apart are left out rather than added as duplicates. Results carry annotations that name both situations directly, so a device marked "MAC address not found" or "Multiple occurrences for the same MAC" is telling you which of the two you are looking at.
The remaining causes are easier to spot and easier to fix. Recurring scans absorb most of them, because a device missed in one pass tends to appear in the next, and that same rhythm is how unauthorized devices surface once the baseline is stable.
Look for these first:
InvGate Asset Management gives IT teams one interface for hardware, software and cloud assets, covering the full lifecycle from the moment a device is found to the moment it is retired. It combines network scanning, agent based collection and integrations with the platforms that already hold parts of the estate.
Network scanning runs through Discovery Sources, the mechanism the platform uses to bring devices in without anyone touching them. InvGate Discovery is the source that scans your network directly, and it runs through a lightweight proxy installed inside the network so nothing needs to be exposed externally. The InvGate Asset Management's Agent is a second Discovery type, deployed from the same section, and its job is filling in depth on the computers where it runs rather than finding new hardware.
The capabilities that matter most for network discovery work are these:
Four steps take you from nothing installed to devices in the inventory. The first two are one time setup per network segment, and the last two are the cycle you repeat.
 The proxy is the component that performs the scan from inside your network and reports results back. Go to Settings > Discovery > Proxies, create a new proxy, download the installer for the operating system it will run on, and execute it on the chosen machine.
Most organizations run one proxy per network, location or segment. That placement matters more than it looks, because a device in a different subnet than the proxy will not have its MAC address read and will not reach the results table.
A configuration window opens after installation and asks for your InvGate Asset Management URL, the proxy security token and a name for the proxy. All three values are available during the process.
Once they are entered, the connection between the proxy and the platform is established and the proxy is ready to run scans. Nothing else needs to be installed on the machines being scanned.
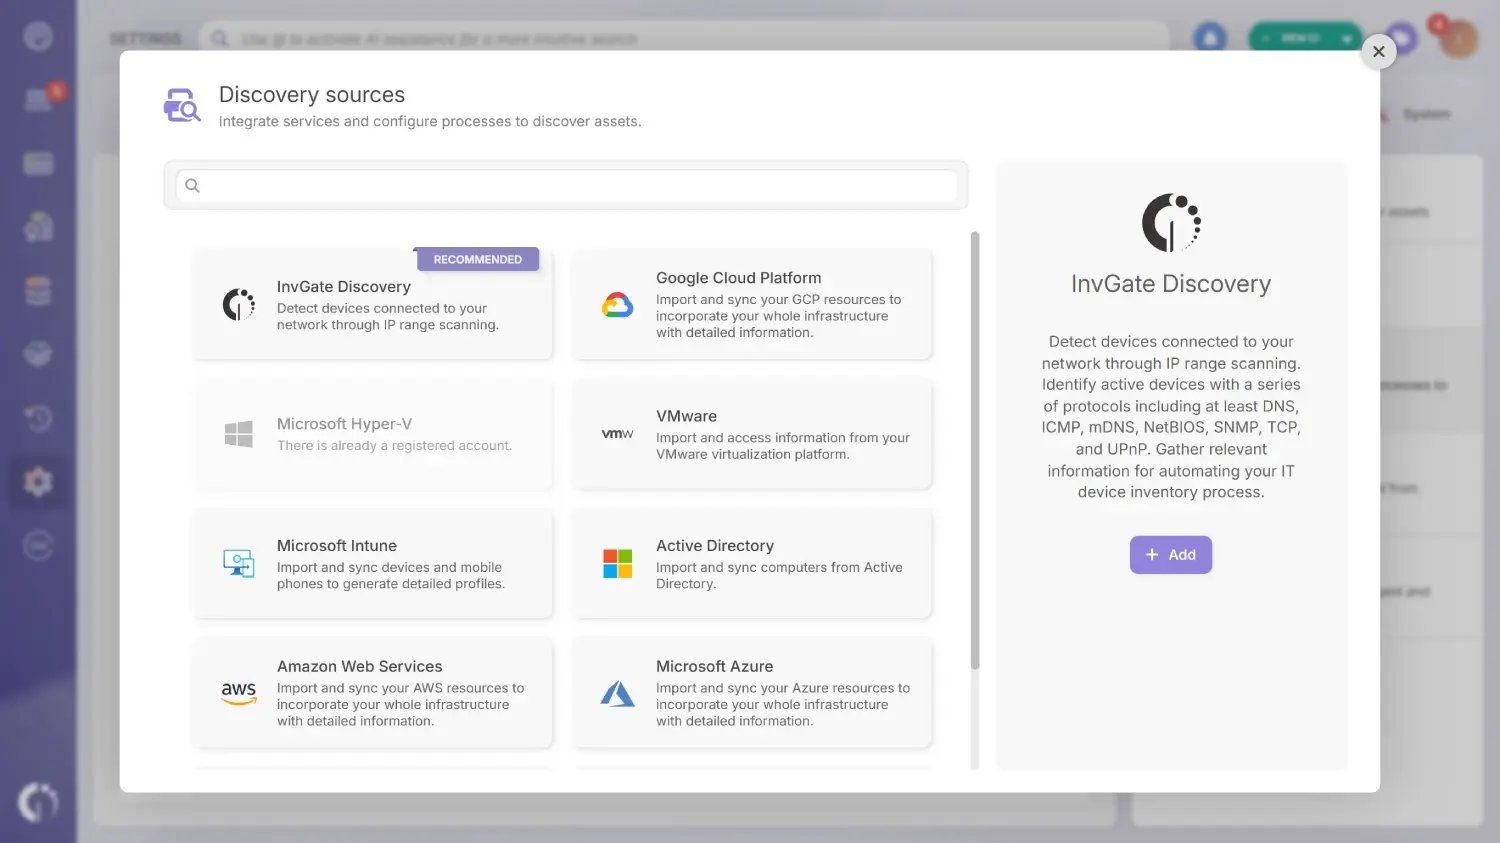 Go to Settings > Discovery > Discovery sources, click Add, and choose InvGate Discovery. Here you pick the proxy that will run the scan, the address ranges to cover, the protocols to use, and the schedule, including start date, time and frequency.
Protocol selection is the setting worth revisiting later. Each execution writes a log with the number of devices found and updated, and a downloadable file listing which addresses responded and what was detected for each, which is the fastest way to see whether a protocol is worth enabling.
 Detected devices appear under Assets > Discovery, each carrying its status, source, conflicts against existing assets, and annotations explaining anything unusual. From here you can convert devices into assets, use Select similar assets to group everything of the same kind and source, or Set as ignored to keep hardware you do not track out of the list without deleting it.
Selecting a single device and clicking Convert to asset opens a form with values suggested from what discovery collected. Selecting several and clicking Convert item(s) opens an editable table instead, which is considerably faster for a first inventory.
A scan that reaches switches over SNMP can do more than list them. It reads each interface and reports what is connected to it, which turns a flat list of addresses into a picture of how the network is actually wired.
The mapping reads Cisco Discovery Protocol (CDP), Link Layer Discovery Protocol (LLDP) and the switch's own MAC address tables, in that order of precedence, then matches what it collects against everything the platform already knows. A few conditions are worth knowing before relying on it:
Although it's not a dedicated network discovery tool, InvGate Asset Management's network scanning covers what is reachable on the wire, and a good deal of the estate lives in systems that already track it. Discovery Sources also pull from those platforms directly, covering Active Directory, Amazon Web Services (AWS), Microsoft Azure, Google Cloud Platform, Microsoft Hyper-V, VMware, Kubernetes, Microsoft Intune, JAMF and SOTI MobiControl. Cloud instances in particular belong to their own integration rather than to a network scan.
Running several sources against one inventory is what closes the remaining gaps, since a device invisible to one source is usually well documented by another. To see how this works on your own network, start a 30-day free trial of InvGate Asset Management, or talk to Sales about scanning a larger or segmented environment.
Connect our solutions with the apps you use every day.
Explore InvGate's integrations
Network discovery answers one question well: what is connected to this network right now. It answers it without touching a single device, which is why it reaches the printers, switches and appliances that no agent will ever run on.
Turning those answers into an inventory takes the step most guides skip. A scan produces addresses and attributes, and reconciliation, ownership and lifecycle data turn them into records a team can manage, audit and plan against.
No. The Windows setting controls whether one computer is visible to others on a local network, and it is configured per machine. The practice described here scans a network from a central tool to build an inventory of everything connected to it.
No. Network discovery is agentless by definition and collects what devices expose over the network. Agents are a separate method that adds depth on computers, particularly installed software and usage data.
The device name and type, IP address, MAC address, manufacturer, model, serial number, interfaces, uptime, contact and location, plus supply levels on printers. How much of that arrives depends on which protocols are enabled and whether read credentials are configured.
Discovery identifies devices by MAC address. A device in a different subnet than the scanning proxy will not have its MAC read, and devices behind a Proxy ARP configuration all report the same MAC, so neither group can be added to the results.
Often enough to keep pace with how fast the network changes, which for most organizations means weekly or daily. A single scan is accurate on the day it runs and degrades from there as devices are added, moved and retired.

